Our blog

Resources and Insights

What changed in European compliance, what it requires, and what to do about it.

Frameworks

Reglamento de IA: qué hacer si tu empresa usa IA

Riesgos, IA no declarada y un plan en cinco pasos, con los plazos tras el Ómnibus Digital.

Àngela Vercher

Àngela Vercher

05.11.26

Actualités et analyses

RGPD, DORA, NIS2: une conformité qui se joue localement

Pourquoi Formalize s'installe à Paris, et pourquoi Excel ne suffit plus.

Maurice Müller

Maurice Müller

21.10.26

Notícias e Análises

Konica Minolta e Formalize unem-se em Portugal

Consultoria, implementação e serviços geridos numa única plataforma de GRC.

Àngela Vercher

Àngela Vercher

20.10.26

News

Cyberincident bij Albert Heijn: vijf lessen voor organisaties

Wat één shutdown laat zien over weerbaarheid, leveranciers en melden.

Laura Eck

Laura Eck

20.10.26

Frameworks

NISG 2026 in Österreich: Was jetzt gilt und bis wann

Meldepflicht seit 1. Oktober, Registrierung bis Jahresende: der Überblick.

Sarah Mille

Sarah Mille

19.10.26

Frameworks

Drei Jahre revDSG: Was Schweizer Unternehmen jetzt brauchen

Warum Dokumentieren nicht mehr reicht und was der EDÖB jetzt prüft.

Sarah Mille

Sarah Mille

15.10.26

Frameworks

NIS2 en France : se préparer sans attendre la loi

Ce que change la saisine de la CJUE, et ce que vous couvrez déjà.

Maurice Müller

Maurice Müller

30.09.26

Frameworks

NIS2 en España: qué significa la remisión al TJUE y cómo cumplir ya

Qué significa la remisión al TJUE, y cómo tu ISO 27001 y ENS ya cubren gran parte del Artículo 21.

Àngela Vercher

Àngela Vercher

22.09.26

Design

Migrating to Linear 101 English

Italian description

Design

PM mental models

Sub header placeholder title example placeholder title example placeholder title example placeholder title example placeholder title example placeholder title example placeholder title example

News & Analysis

Supermarket Fridge Cyberattacks: What Happened and What to Check Now

Attackers changed refrigeration settings in hundreds of European stores. The confirmed facts, the EU rules that apply and the checks authorities recommend.

Maurice Müller

Maurice Müller

06.11.26

News & Analysis

Frontier AI and Digital Resilience: Governance Can't Wait

What the Bank of Italy expects in the Report due on 31 December 2026, area by area.

Alessia Gilardi

Alessia Gilardi

06.11.26

Frameworks

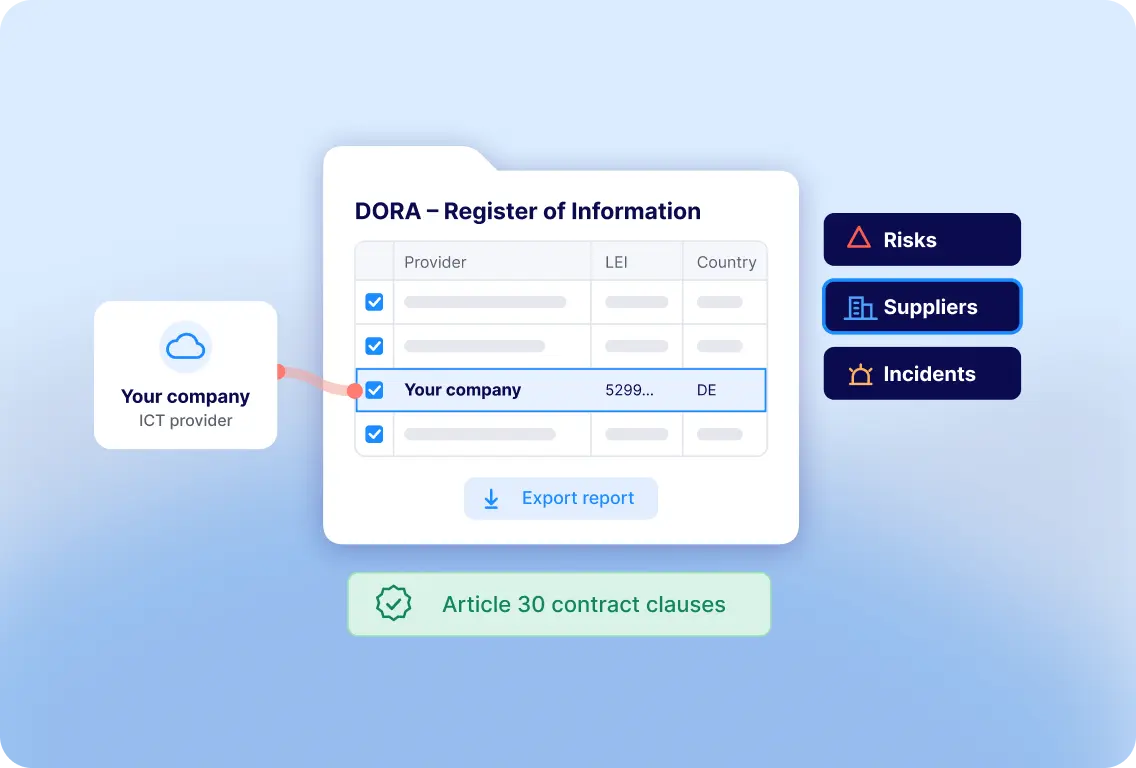
DORA for ICT Providers: What Financial Clients Expect

The contract clauses, evidence and data your financial clients need from you, and how to prepare.

Maurice Müller

Maurice Müller

05.11.26

Frameworks

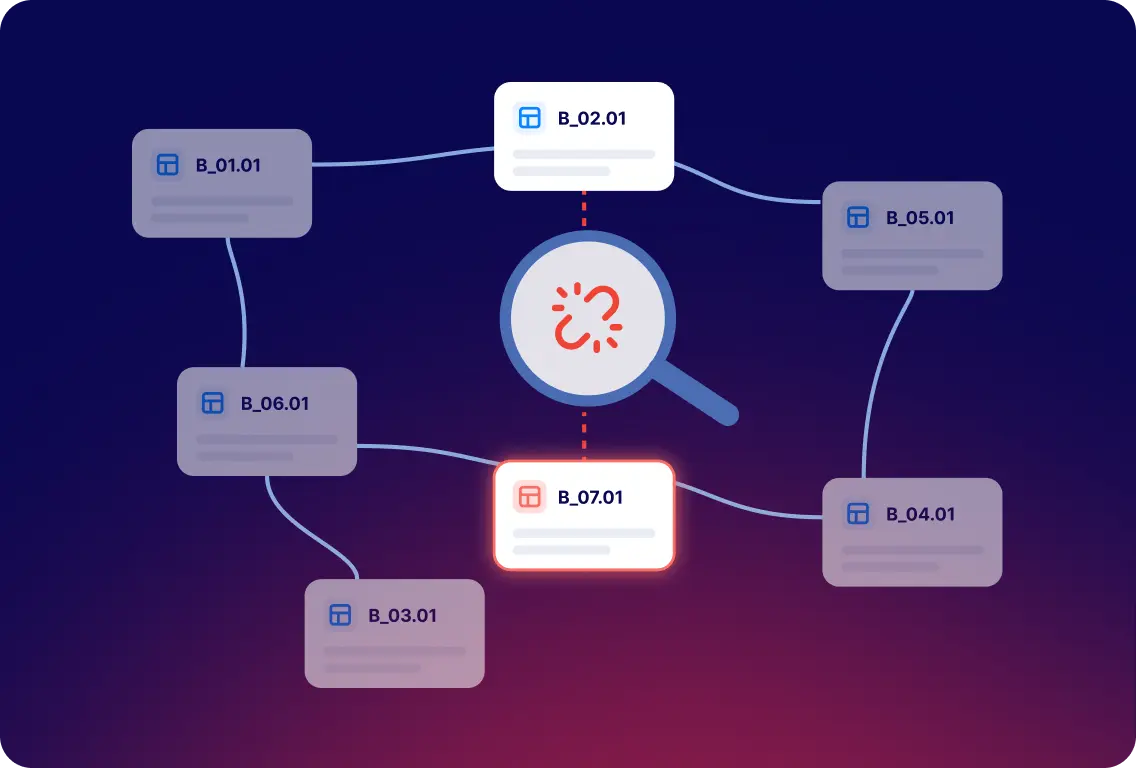
DORA Register of Information: Fixing Validation Errors

What each error means, who owns the fix, and what to check before you submit.

Maurice Müller

Maurice Müller

03.11.26

Risk & Governance

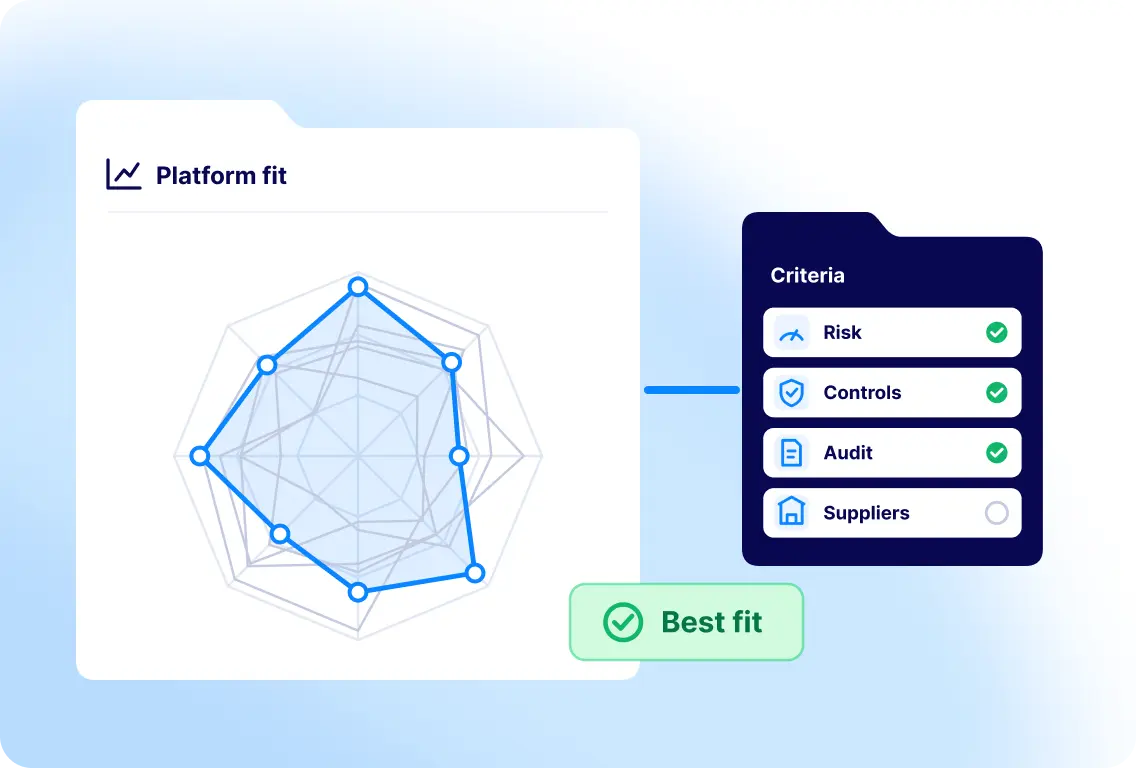
Best GRC Software in 2026: Six Platforms Compared

Which GRC platform fits your program, and what to check in the demo.

Maurice Müller

Maurice Müller

02.11.26

News & Analysis

PHP2Shell: When AI Finds the Flaws First

What happened on 21 October, and the lessons for security and compliance teams.

Maurice Müller

Maurice Müller

30.10.26

Frameworks

What a SOC 2 Report Verifies and What It Does Not Verify

Criteria for trust services: Type 1 vs Type 2, and how to prepare for an audit.

Maurice Müller

Maurice Müller

21.10.26

Risk & Governance

Policy Management: From Shared Drive to Audit Trail

The seven-step lifecycle, what makes it work, and when software helps.

Maurice Müller

Maurice Müller

20.10.26

Frameworks

Blueprint ISO 42001: governance dell'IA con Rexilience

Cosa richiede la ISO 42001 e come il nuovo Blueprint ti aiuta ad applicarla.

Alessia Gilardi

Alessia Gilardi

16.10.26

Platform

Internal Audit Findings: How to Make Sure They Get Fixed

Five checks that make sure audit findings get closed, not forgotten.

Maurice Müller

Maurice Müller

12.10.26

Frameworks

GDPR Compliance Means Being Able to Prove It

The principles, a 10-step checklist, and what changes in 2026 and 2027.

Maurice Müller

Maurice Müller

07.10.26

News & Analysis

When an AI Agent Causes a Data Breach

Why incident response and AI governance can no longer run separately.

Alessia Gilardi

Alessia Gilardi

29.09.26

Risk & Governance

Data Governance: Who Decides What Happens to Your Data

Frameworks, functions, and the steps for putting data-related rules into daily practice.

Maurice Müller

Maurice Müller

29.09.26

Frameworks

Cyber Resilience Act: The New 24-Hour Reporting Rule

Who it applies to, what it covers, and how it overlaps with NIS2 and GDPR.

Àngela Vercher

Àngela Vercher

28.09.26

Frameworks

DORA Regulation: What Still Needs Proving Now

The five pillars, the penalties, and what changed since the deadline.

Maurice Müller

Maurice Müller

24.09.26

News & Analysis

When Verification Fails: A GDPR Breach Case

The control that would have stopped it, and why most policies lack it.

Laura Santeusanio

Laura Santeusanio

23.09.26

Frameworks

What Is a DPIA? GDPR's Privacy Risk Assessment, Explained

Discover how to spot Article 35 triggers, the 7 steps, and what to include.

Maurice Müller

Maurice Müller

21.09.26

Frameworks

NIS2 in Italy: "Compliant on Paper" Won't Survive October

The 10 required measures, the fines, and how to close the gap in time.

Laura Santeusanio

Laura Santeusanio

18.09.26

Platform

Compliance Management Software: What to Look For

What the software does, the real benefits, and how to compare platforms.

Maurice Müller

Maurice Müller

16.09.26

Risk & Governance

What Is AI Risk Management?

Main risk types, the NIST framework, and a 6-step process to follow.

Maurice Müller

Maurice Müller

14.09.26

Risk & Governance

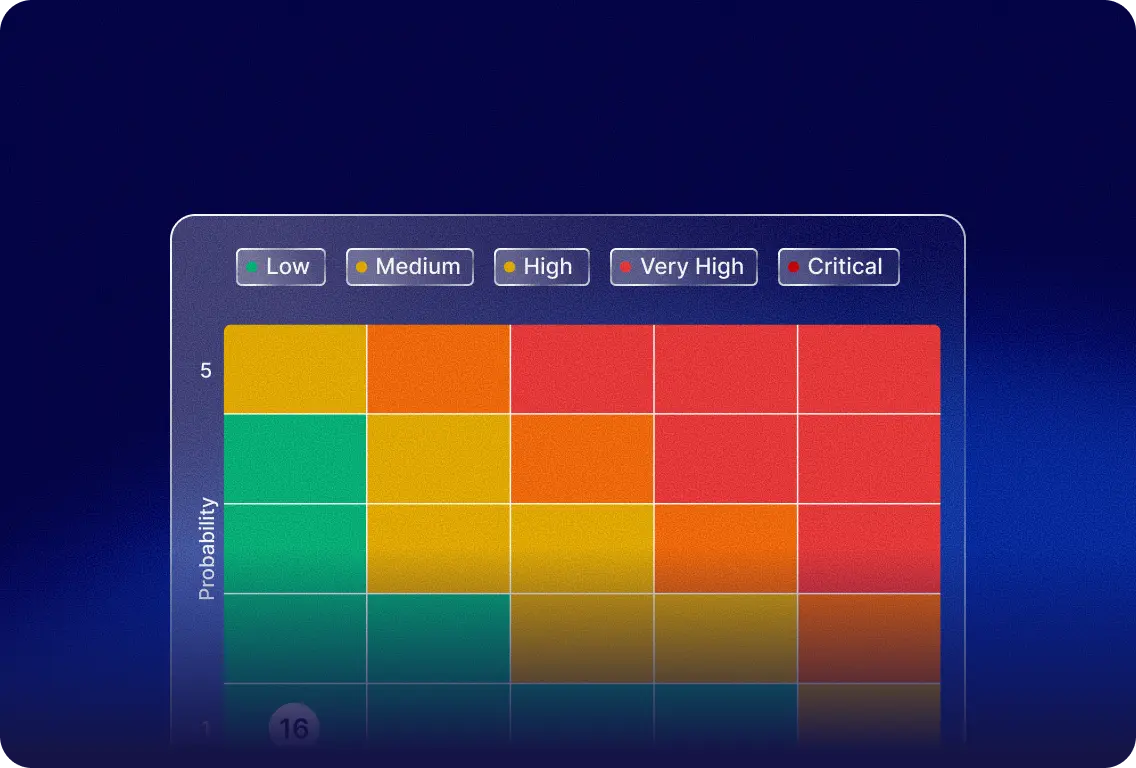
What Is a Risk Matrix? Scoring Explained

How likelihood and impact combine into a score, with a 5x5 example.

Maurice Müller

Maurice Müller

09.09.26

Risk & Governance

What Is Supplier Risk Management? A Practical Guide

How to assess, score, and monitor supplier risk, step by step.

Maurice Müller

Maurice Müller

04.09.26

NIS-2

CSG und CSV in Liechtenstein: Der Leitfaden

CSG und CSV setzen NIS-2 in liechtensteinisches Recht um. Das Wichtigste kompakt.

Sarah Mille

Sarah Mille

01.09.26

Platform

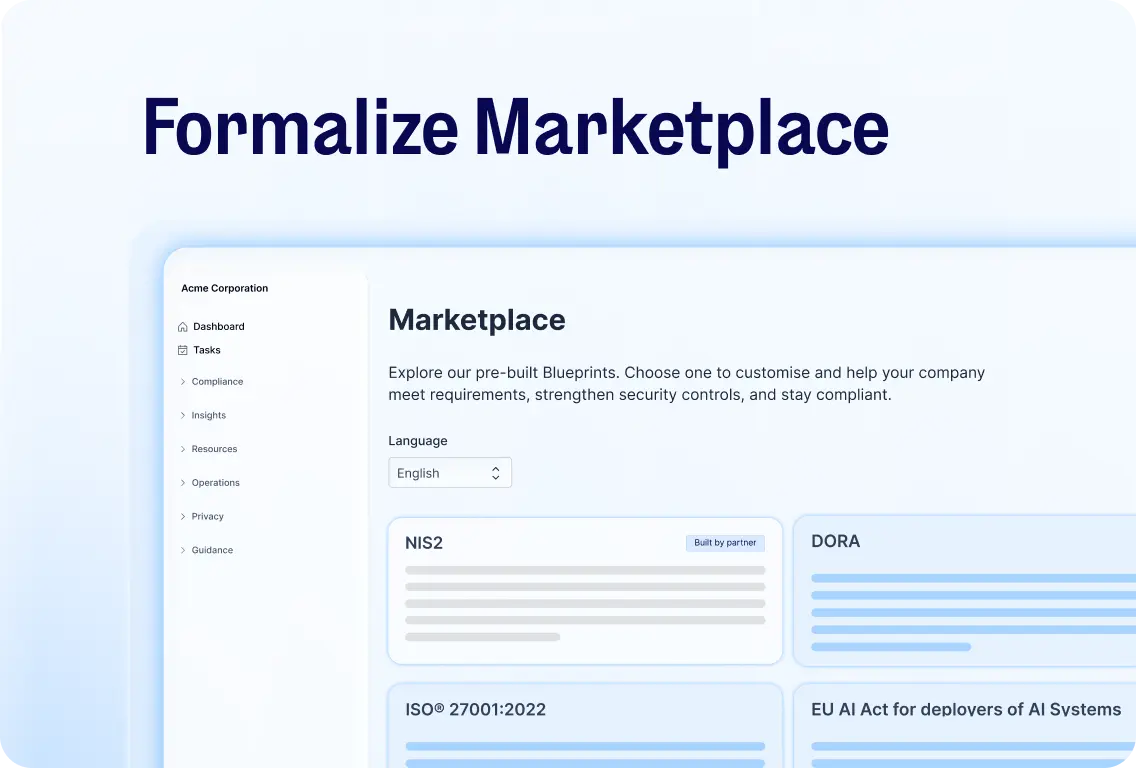
Formalize Marketplace: How Blueprints Work

Partners co-build ready-to-deploy blueprints, so you skip the blank page.

Maurice Müller

Maurice Müller

02.09.26

Risk & Governance

Risk Management Frameworks: Types, Steps & Examples

NIST, ISO 31000, or COSO: compare the frameworks and pick one that fits.

Maurice Müller

Maurice Müller

01.09.26

Frameworks

NIS2 Requirements: Key Pillars & Checklist

What NIS2 actually requires, and how to check where your organization stands.

Maurice Müller

Maurice Müller

25.08.26

Platform

Your Controls Were Right. Are They Still?

AI that reads the actual ISO 27001 standard, not just summaries about it.
Maurice Müller

Maurice Müller

24.08.26

Platform

Stop Digging for Answers. Start Asking.

Your compliance records can finally answer questions, not just sit there.

Maurice Müller

Maurice Müller

24.08.26

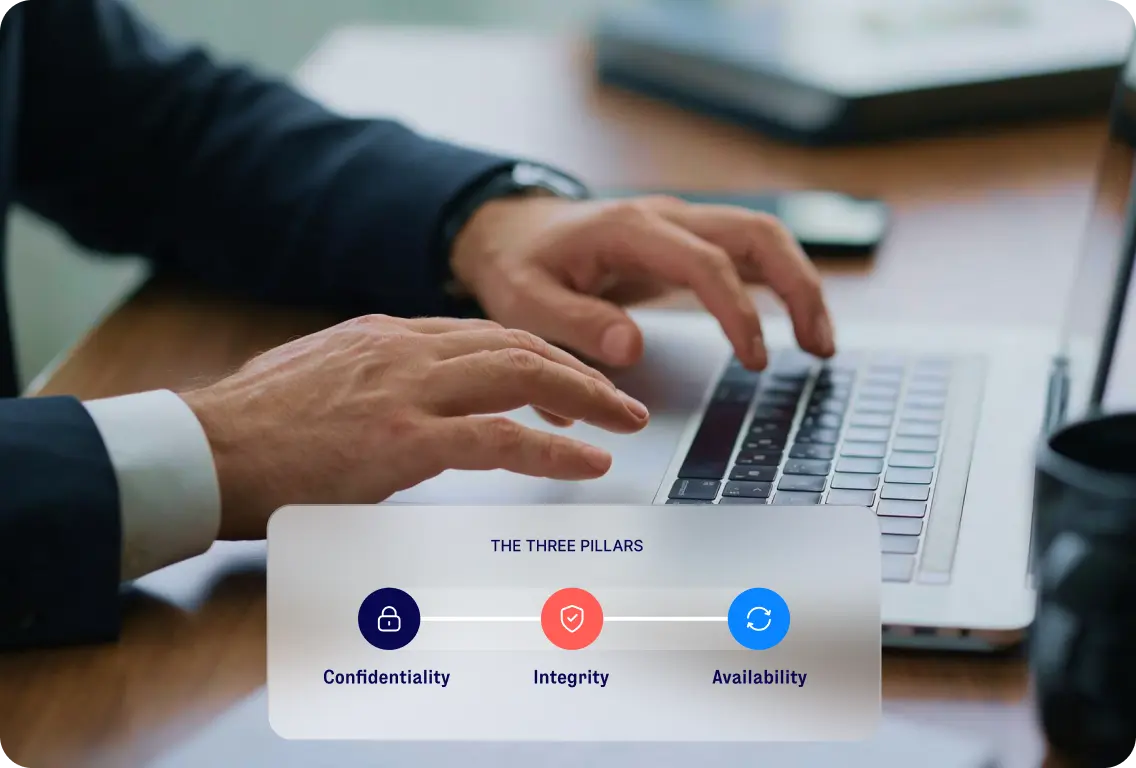
Person typing on a laptop, with an overlay showing the three pillars of information security: confidentiality, integrity, and availability.
Frameworks

What is ISO 27001? ISMS Standard & Compliance Explained

ISO 27001 is the international standard for managing information security risk.

Maurice Müller

Maurice Müller

20.08.26

Frameworks

EU AI Act: What the Digital Omnibus changed, and what it means for your organisation

The EU AI Act's Digital Omnibus has extended key compliance deadlines for high-risk AI systems. The headline is easy to misread: this is not a pause. The obligations remain. The timeline shifted.
Maurice Müller

Maurice Müller

18.08.2026

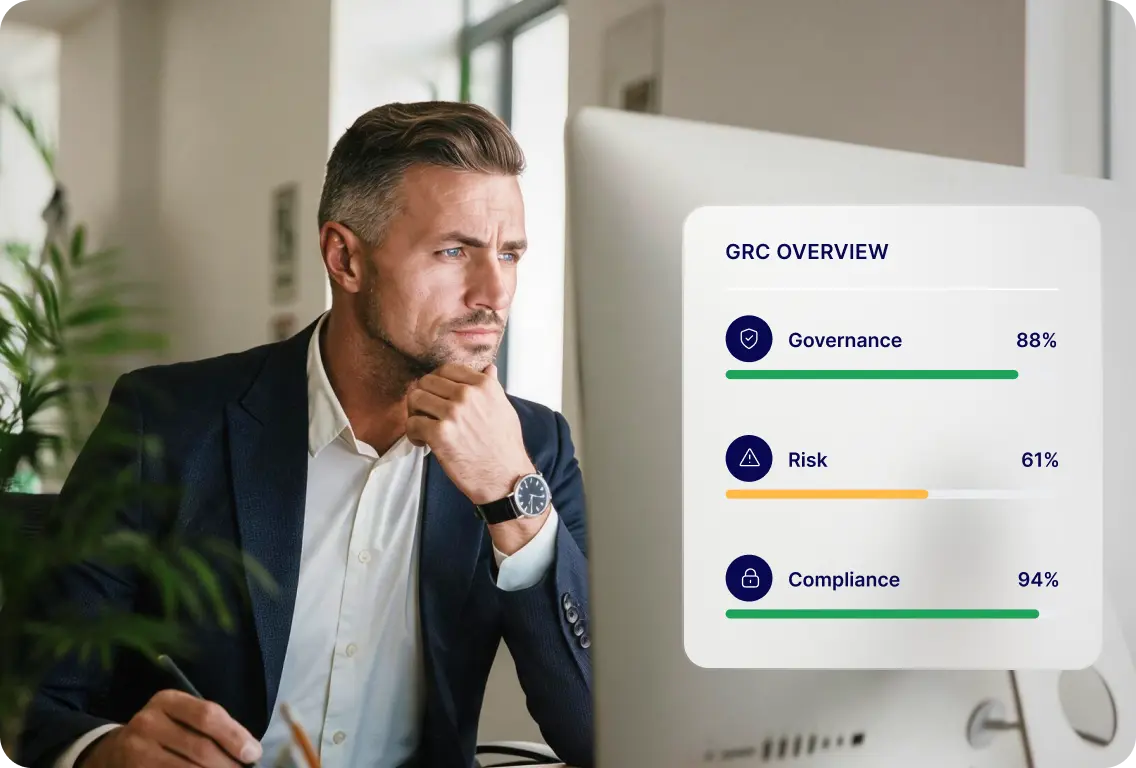
Professional reviewing a GRC dashboard showing governance, risk, and compliance metrics.
Risk & Governance

What is GRC? Governance, Risk, and Compliance Explained

GRC stands for Governance, Risk, and Compliance. The GRC meaning goes beyond the acronym: it describes how organisations structure their internal rules, manage uncertainty, and meet external regulatory requirements, not as three separate workstreams, but as one connected approach.

Maurice Müller

Maurice Müller

31.07.2026

Team working in a meeting room, with a colleague holding a laptop in the foreground.
Frameworks

What is NIS2? The EU cybersecurity directive, and what it means for your organization

NIS2 is the EU's updated directive on network and information security. It sets binding cybersecurity requirements for organizations across critical sectors in Europe, and since October 2024, it is in force.

Maurice Müller

Maurice Müller

31.07.26

Design

Migrating to Linear 101 English

Italian description

Test

Test Simon

test

Book a demo