Ons blog

Bronnen en inzichten

Wat is er veranderd op het gebied van Europese compliance, wat houdt dit in en wat moet er gebeuren?

Frameworks

Reglamento de IA: qué hacer si tu empresa usa IA

Riesgos, IA no declarada y un plan en cinco pasos, con los plazos tras el Ómnibus Digital.

Àngela Vercher

Àngela Vercher

05.11.26

Actualités et analyses

RGPD, DORA, NIS2: une conformité qui se joue localement

Pourquoi Formalize s'installe à Paris, et pourquoi Excel ne suffit plus.

Maurice Müller

Maurice Müller

21.10.26

Notícias e Análises

Konica Minolta e Formalize unem-se em Portugal

Consultoria, implementação e serviços geridos numa única plataforma de GRC.

Àngela Vercher

Àngela Vercher

20.10.26

Nieuws & Analyse

Cyberincident bij Albert Heijn: vijf lessen voor organisaties
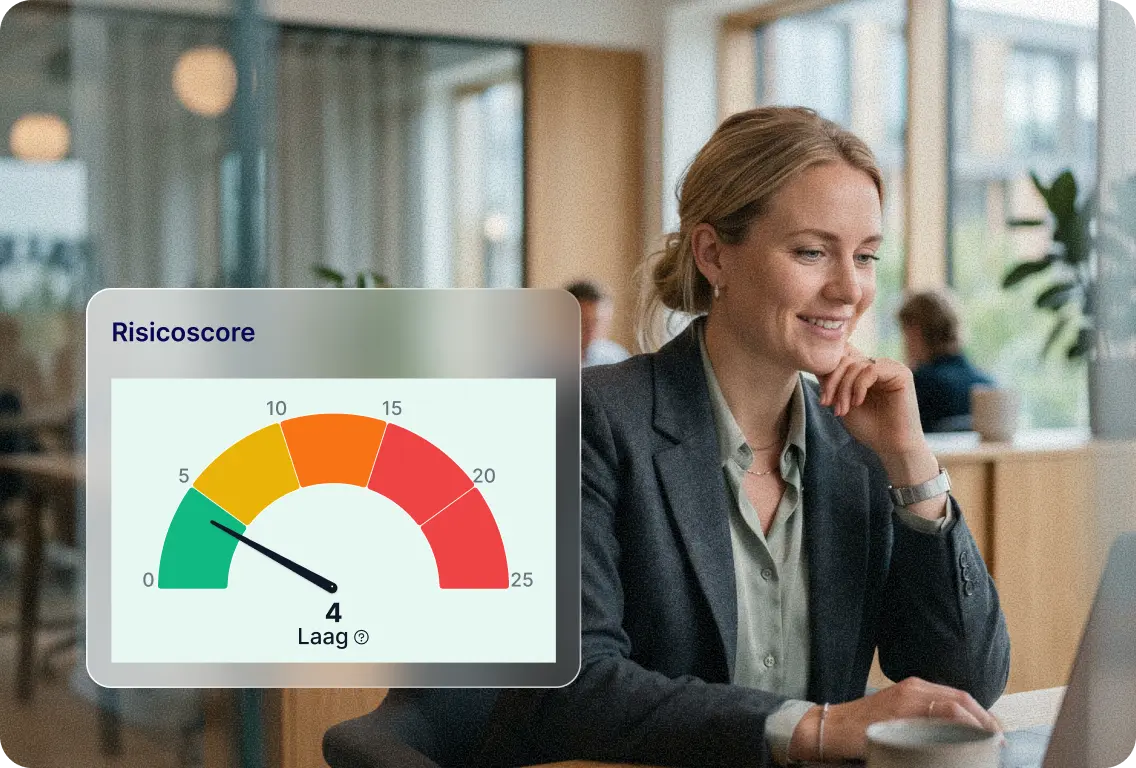
Wat één shutdown laat zien over weerbaarheid, leveranciers en melden.

Laura Eck

Laura Eck

20.10.26

Frameworks

NISG 2026 in Österreich: Was jetzt gilt und bis wann

Meldepflicht seit 1. Oktober, Registrierung bis Jahresende: der Überblick.

Sarah Mille

Sarah Mille

19.10.26

Frameworks

Drei Jahre revDSG: Was Schweizer Unternehmen jetzt brauchen

Warum Dokumentieren nicht mehr reicht und was der EDÖB jetzt prüft.

Sarah Mille

Sarah Mille

15.10.26

NIS2

NIS2 en France : se préparer sans attendre la loi

Ce que change la saisine de la CJUE, et ce que vous couvrez déjà.

Maurice Müller

Maurice Müller

30.09.26

Frameworks

NIS2 en España: qué significa la remisión al TJUE y cómo cumplir ya

Qué significa la remisión al TJUE, y cómo tu ISO 27001 y ENS ya cubren gran parte del Artículo 21.

Àngela Vercher

Àngela Vercher

22.09.26

Design

Migrating to Linear 101 English

Italian description

Design

PM mental models

Sub header placeholder title example placeholder title example placeholder title example placeholder title example placeholder title example placeholder title example placeholder title example

News & Analysis

Supermarket Fridge Cyberattacks: What Happened and What to Check Now

Attackers changed refrigeration settings in hundreds of European stores. The confirmed facts, the EU rules that apply and the checks authorities recommend.
Maurice Müller

Maurice Müller

06.11.26

News & Analysis

Frontier AI and Digital Resilience: Governance Can't Wait

What the Bank of Italy expects in the Report due on 31 December 2026, area by area.

Alessia Gilardi

Alessia Gilardi

06.11.26

Frameworks

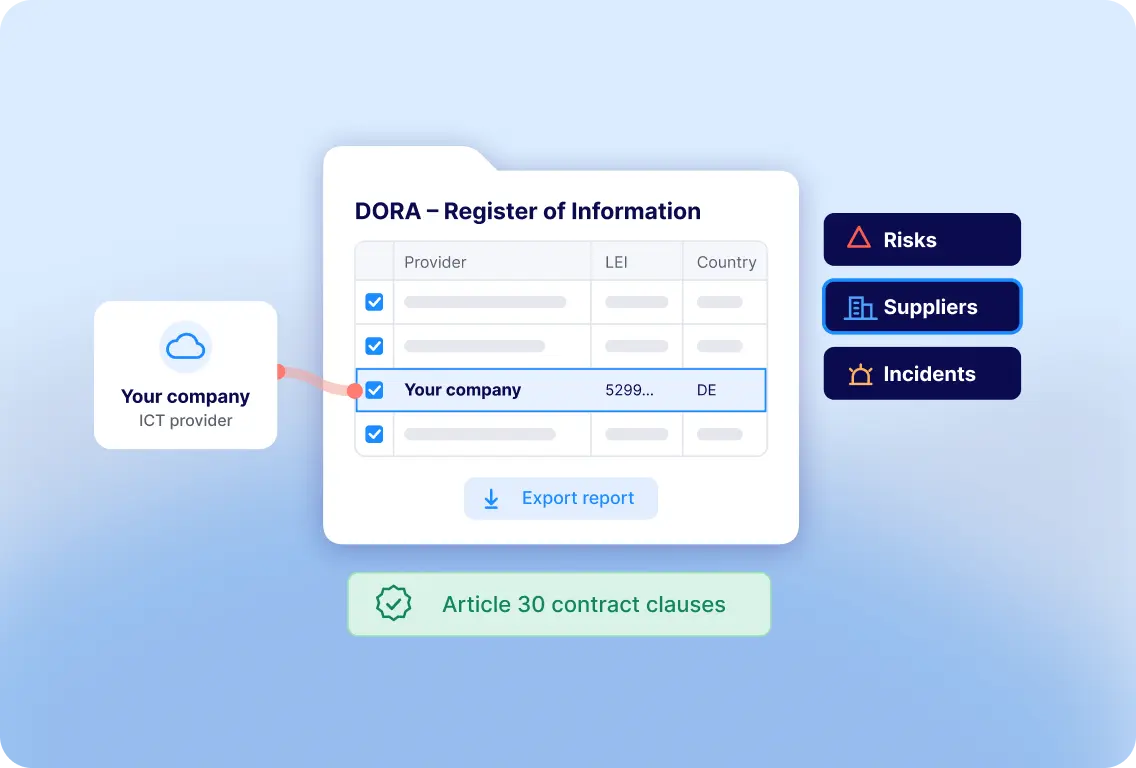
DORA for ICT Providers: What Financial Clients Expect

The contract clauses, evidence and data your financial clients need from you, and how to prepare.

Maurice Müller

Maurice Müller

05.11.26

Frameworks

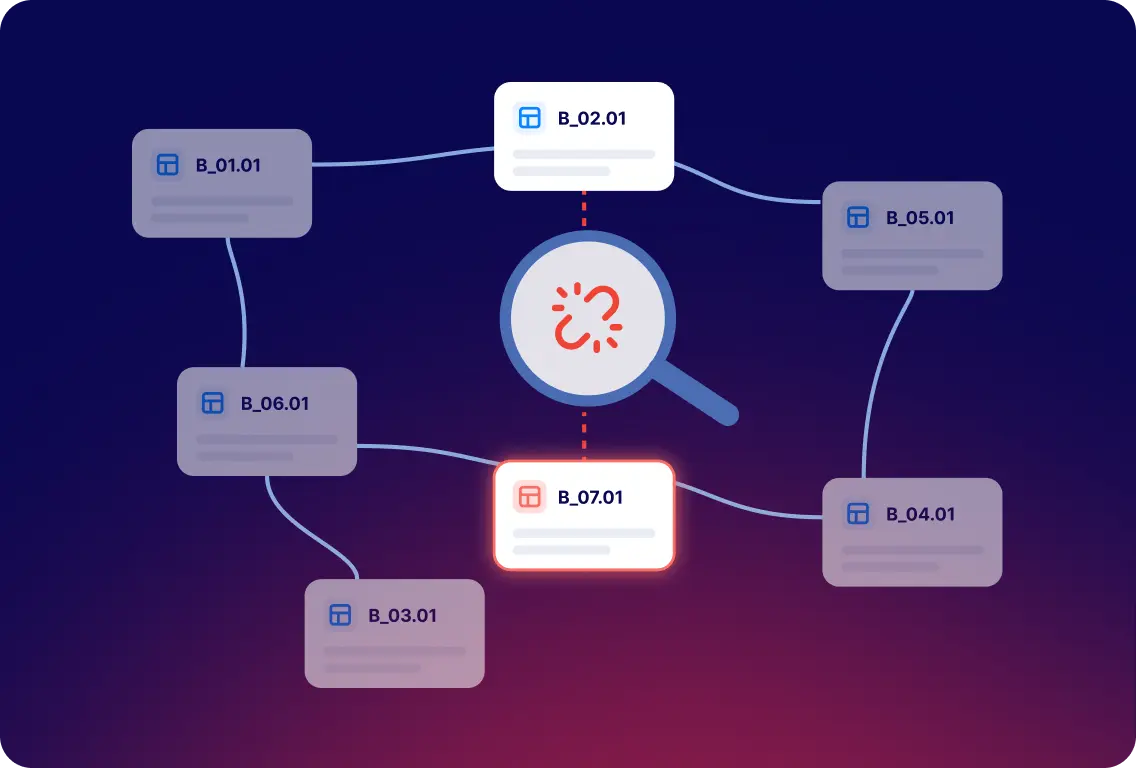
DORA Register of Information: Fixing Validation Errors

What each error means, who owns the fix, and what to check before you submit.

Maurice Müller

Maurice Müller

03.11.26

Risk & Governance

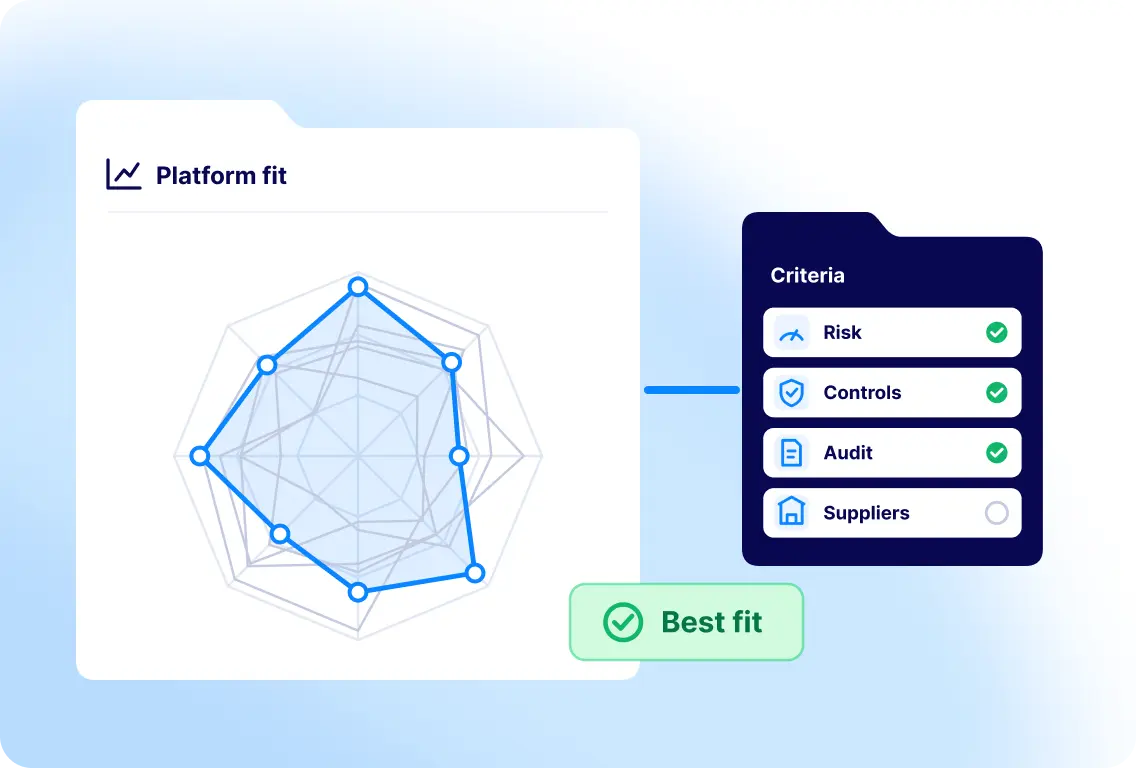
Best GRC Software in 2026: Six Platforms Compared

Which GRC platform fits your program, and what to check in the demo.

Maurice Müller

Maurice Müller

02.11.26

News & Analysis

PHP2Shell: When AI Finds the Flaws First

What happened on 21 October, and the lessons for security and compliance teams.

Maurice Müller

Maurice Müller

30.10.26

Frameworks

What a SOC 2 Report Verifies and What It Does Not Verify

Criteria for trust services: Type 1 vs Type 2, and how to prepare for an audit.

Maurice Müller

Maurice Müller

21.10.26

Risk & Governance

Policy Management: From Shared Drive to Audit Trail

The seven-step lifecycle, what makes it work, and when software helps.

Maurice Müller

Maurice Müller

20.10.26

Frameworks

Blueprint ISO 42001: governance dell'IA con Rexilience

Cosa richiede la ISO 42001 e come il nuovo Blueprint ti aiuta ad applicarla.

Alessia Gilardi

Alessia Gilardi

16.10.26

Platform

Bevindingen van de interne audit: Hoe zorgt u ervoor dat er actie wordt ondernomen?

Vijf controles die ervoor zorgen dat auditbevindingen worden afgehandeld en niet worden vergeten.

Maurice Müller

Maurice Müller

12.10.26

Frameworks

GDPR Compliance Means Being Able to Prove It

The principles, a 10-step checklist, and what changes in 2026 and 2027.

Maurice Müller

Maurice Müller

07.10.26

News & Analysis

When an AI Agent Causes a Data Breach

Why incident response and AI governance can no longer run separately.

Alessia Gilardi

Alessia Gilardi

29.09.26

Risk & Governance

Data Governance: Who Decides What Happens to Your Data

Frameworks, functions, and the steps for putting data-related rules into daily practice.

Maurice Müller

Maurice Müller

29.09.26

Frameworks

Cyber Resilience Act: The New 24-Hour Reporting Rule

Who it applies to, what it covers, and how it overlaps with NIS2 and GDPR.

Àngela Vercher

Àngela Vercher

28.09.26

Frameworks

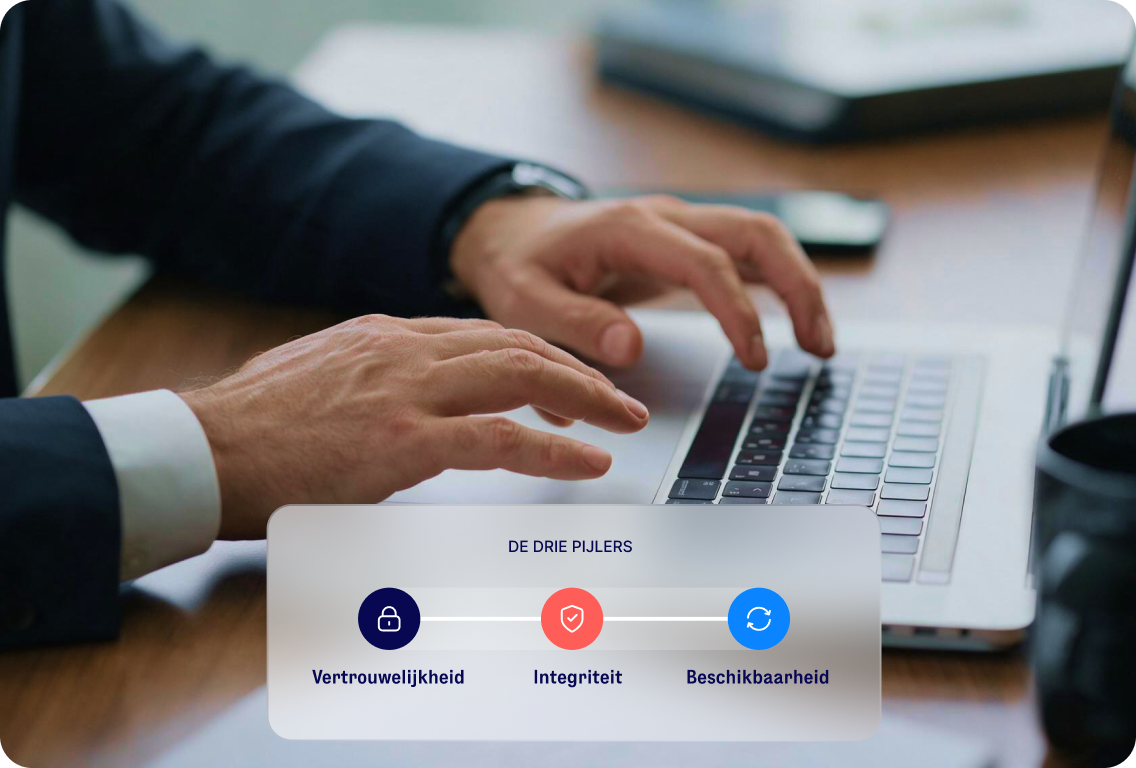
De DORA-verordening: wat er op dit moment nog moet worden aangetoond

De vijf pijlers, de sancties en wat er sinds de deadline is veranderd.

Maurice Müller

Maurice Müller

24.09.26

Nieuws & Analyse

Wanneer verificatie faalt: een AVG-schending uit de praktijk

De controle die dit had kunnen voorkomen, en waarom die in het meeste beleid ontbreekt.

Laura Santeusanio

Laura Santeusanio

23.09.26

Frameworks

Wat is een DPIA? De privacyrisicobeoordeling van de AVG, uitgelegd

Ontdek hoe u signalen herkent die aanleiding geven tot Artikel 35, wat de 7 stappen zijn en wat u daarin moet opnemen.

Maurice Müller

Maurice Müller

21.09.26

Frameworks

NIS2 in Italy: "Compliant on Paper" Won't Survive October

The 10 required measures, the fines, and how to close the gap in time.

Laura Santeusanio

Laura Santeusanio

18.09.26

Platform

Compliance Management Software: What to Look For

What the software does, the real benefits, and how to compare platforms.

Maurice Müller

Maurice Müller

16.09.26

Risico & Governance

Wat is AI-risicobeheer?

De belangrijkste risicotypes, het NIST-framework en een 6-stappenplan dat u kunt volgen.

Maurice Müller

Maurice Müller

14.09.26

Risico & Governance

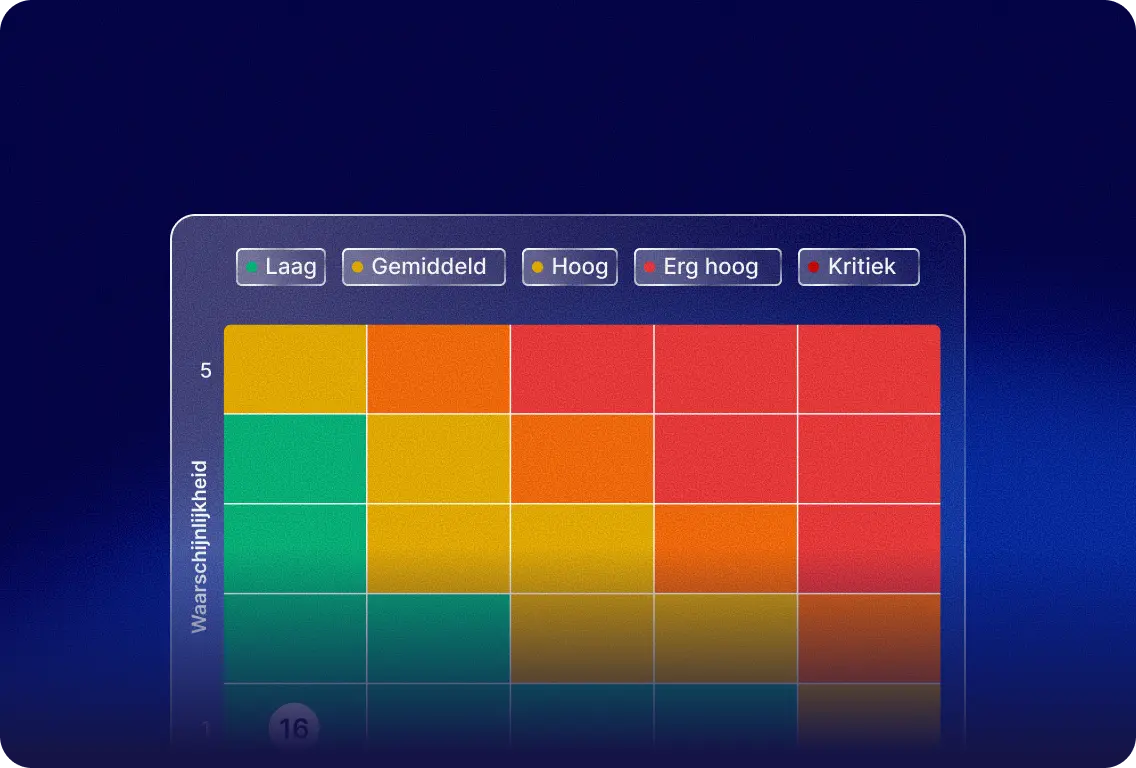
Wat is een risicomatrix? Uitleg over risicoscores

Hoe waarschijnlijkheid en impact samen een score vormen, aan de hand van een voorbeeld van een 5x5-matrix.

Maurice Müller

Maurice Müller

09.09.26

Risico & Governance

Wat is leveranciersrisicobeheer? Een praktische gids

Hoe u leveranciersrisico’s stap voor stap kunt beoordelen, scoren en monitoren.

Maurice Müller

Maurice Müller

04.09.26

NIS-2

CSG und CSV in Liechtenstein: Der Leitfaden

CSG und CSV setzen NIS-2 in liechtensteinisches Recht um. Das Wichtigste kompakt.

Sarah Mille

Sarah Mille

01.09.26

Platform

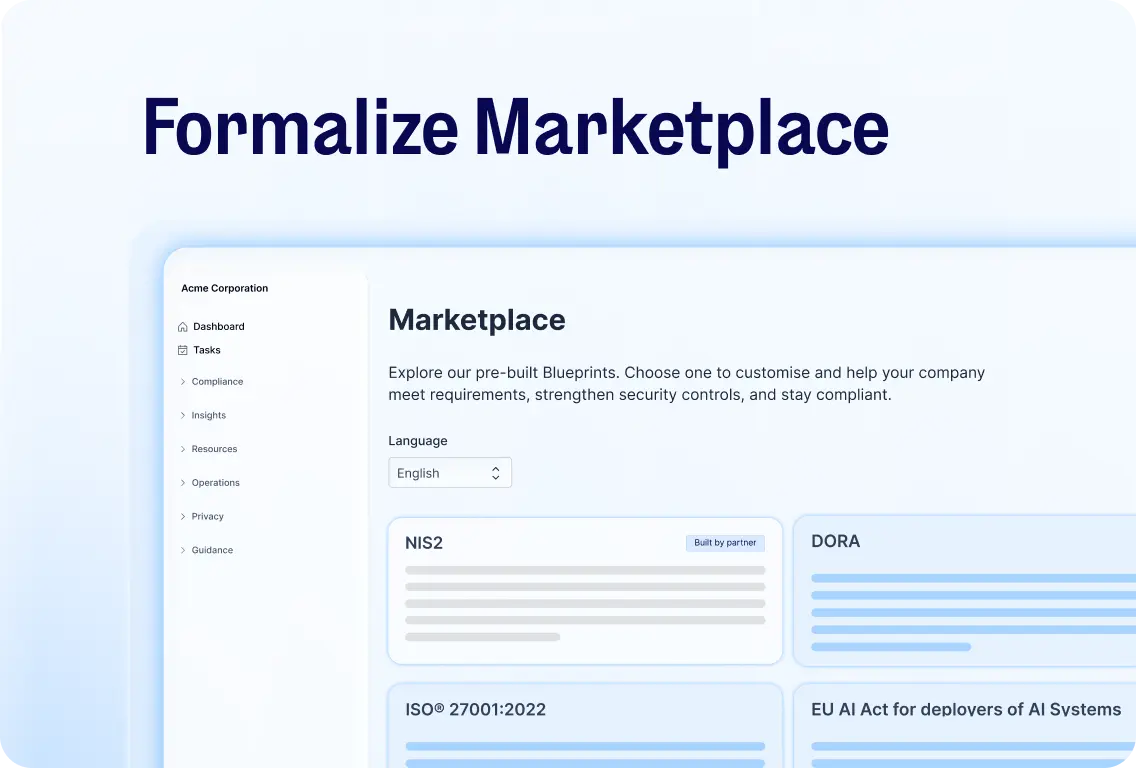
Formalize Marketplace: Hoe Blueprints functioneren

Partners werken samen aan kant-en-klare Blueprints, zodat u niet vanaf nul hoeft te beginnen.

Maurice Müller

Maurice Müller

02.09.26

Risico & Governance

Frameworks voor risicobeheer: Soorten, stappen & voorbeelden

NIST, ISO 31000 of COSO: vergelijk de frameworks en kies het framework dat het beste aansluit..

Maurice Müller

Maurice Müller

01.09.26

Frameworks

NIS 2-vereisten: belangrijkste pijlers & checklist

Wat NIS 2 precies vereist, en hoe u kunt nagaan hoe uw organisatie ervoor staat.

Maurice Müller

Maurice Müller

25.08.26

Platform

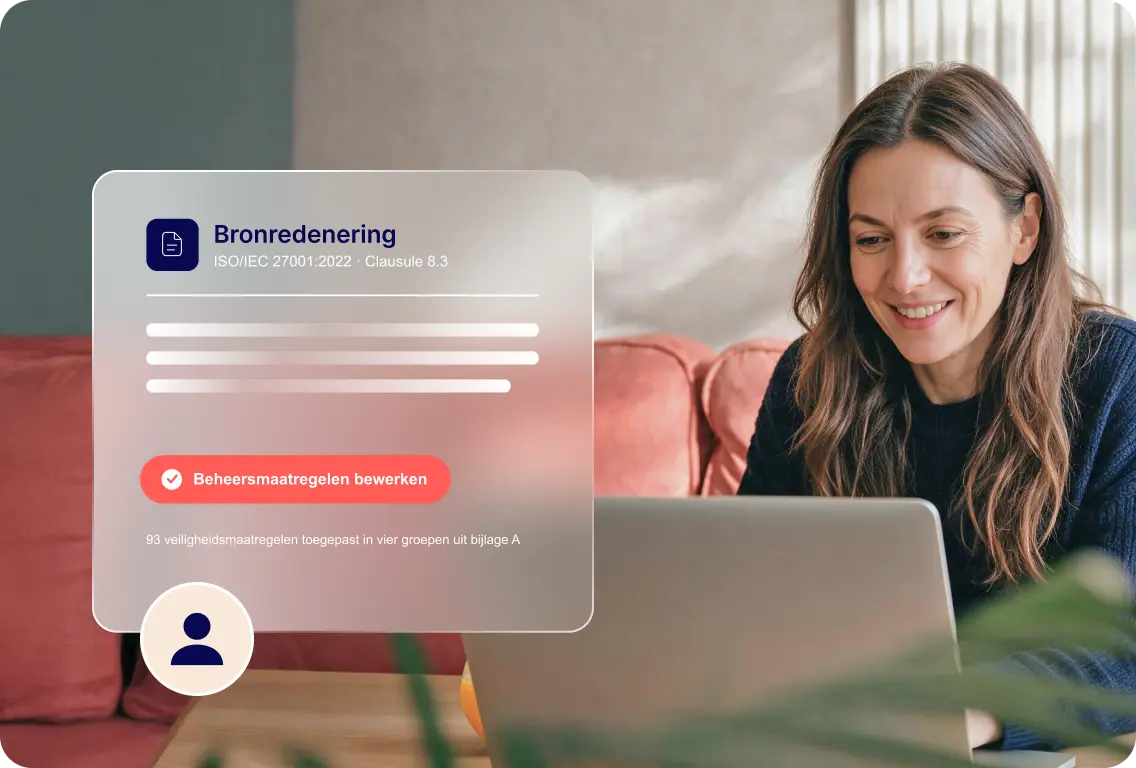
Uw beheersmaatregelen waren juist. Is dat nog steeds zo?

AI die de daadwerkelijke ISO 27001-norm leest, en niet alleen samenvattingen ervan.

Maurice Müller

Maurice Müller

24.08.26

Platform

Stop met zoeken naar antwoorden. Begin met vragen stellen.

Uw compliancegegevens kunnen eindelijk vragen beantwoorden, in plaats van slechts te worden bewaard.

Maurice Müller

Maurice Müller

24.08.26

Frameworks

Wat is ISO 27001? Uitleg over de ISMS-norm & compliance

ISO 27001 is de internationale norm voor het beheer van informatiebeveiligingsrisico's.

Maurice Müller

Maurice Müller

20.08.26

Frameworks

EU AI-verordening: Wat er door de Digital Omnibus is veranderd en wat dit voor uw organisatie betekent

De Digitale Omnibus voor de EU AI-verordening heeft de belangrijkste compliance-deadlines voor AI-systemen met een hoog risico verlengd. De titel kan gemakkelijk verkeerd worden geïnterpreteerd: dit is geen uitstel. De verplichtingen blijven van kracht. Alleen wordt de tijdlijn verschoven.

Maurice Müller

Maurice Müller

18.08.2026

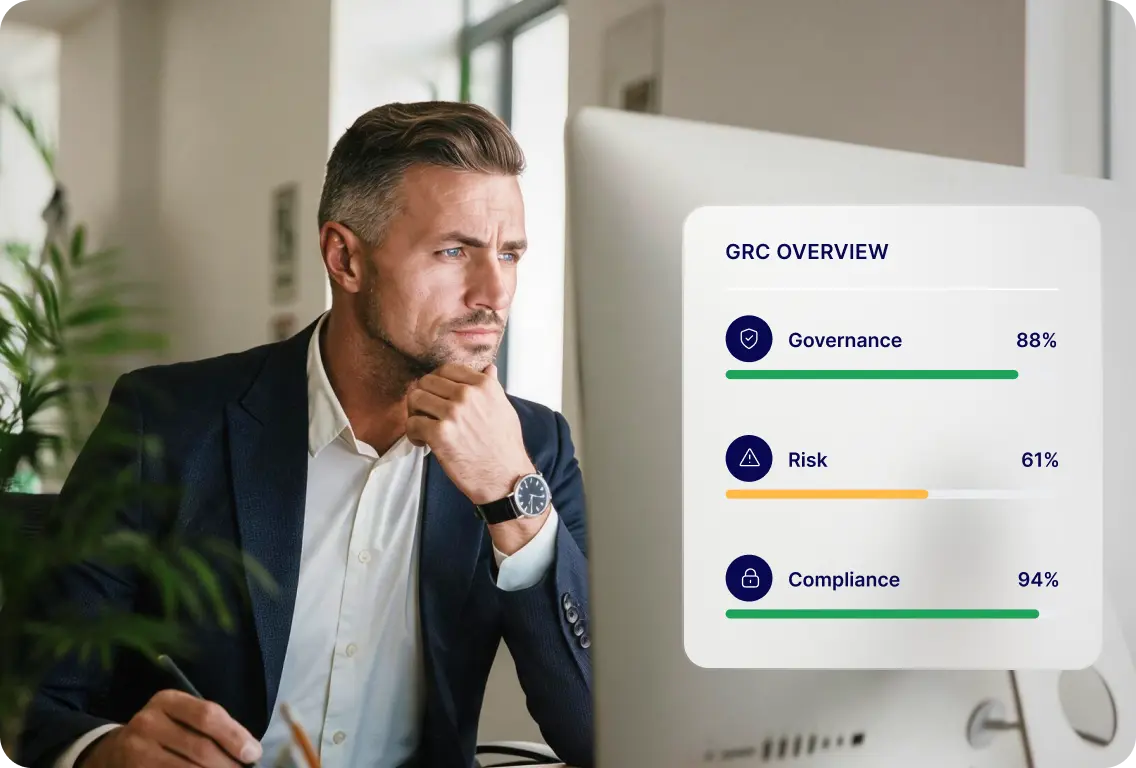
Professional reviewing a GRC dashboard showing governance, risk, and compliance metrics.
Risico & Governance

Wat is GRC? Governance, risico en compliance uitgelegd

GRC staat voor Governance, Risk en Compliance. De betekenis van GRC reikt verder dan de afkorting zelf: het beschrijft hoe organisaties hun interne regels structureren, omgaan met onzekerheid en voldoen aan externe wettelijke vereisten, niet als drie afzonderlijke werkgebieden, maar als één samenhangende aanpak.

Maurice Müller

Maurice Müller

31.07.2026

Team working in a meeting room, with a colleague holding a laptop in the foreground.
Frameworks

Wat is NIS 2? De EU-richtlijn inzake cyberbeveiliging en wat deze voor uw organisatie betekent

NIS 2 is de herziene EU-richtlijn inzake netwerk- en informatiebeveiliging. Deze richtlijn stelt bindende cyberbeveiligingseisen vast voor organisaties in kritieke sectoren in Europa en is sinds oktober 2024 van kracht.

Maurice Müller

Maurice Müller

31.07.26

Design

Migrating to Linear 101 English

Italian description

Test

Test Simon

test

Boek een demo