GDPR software that shows every risk in one place
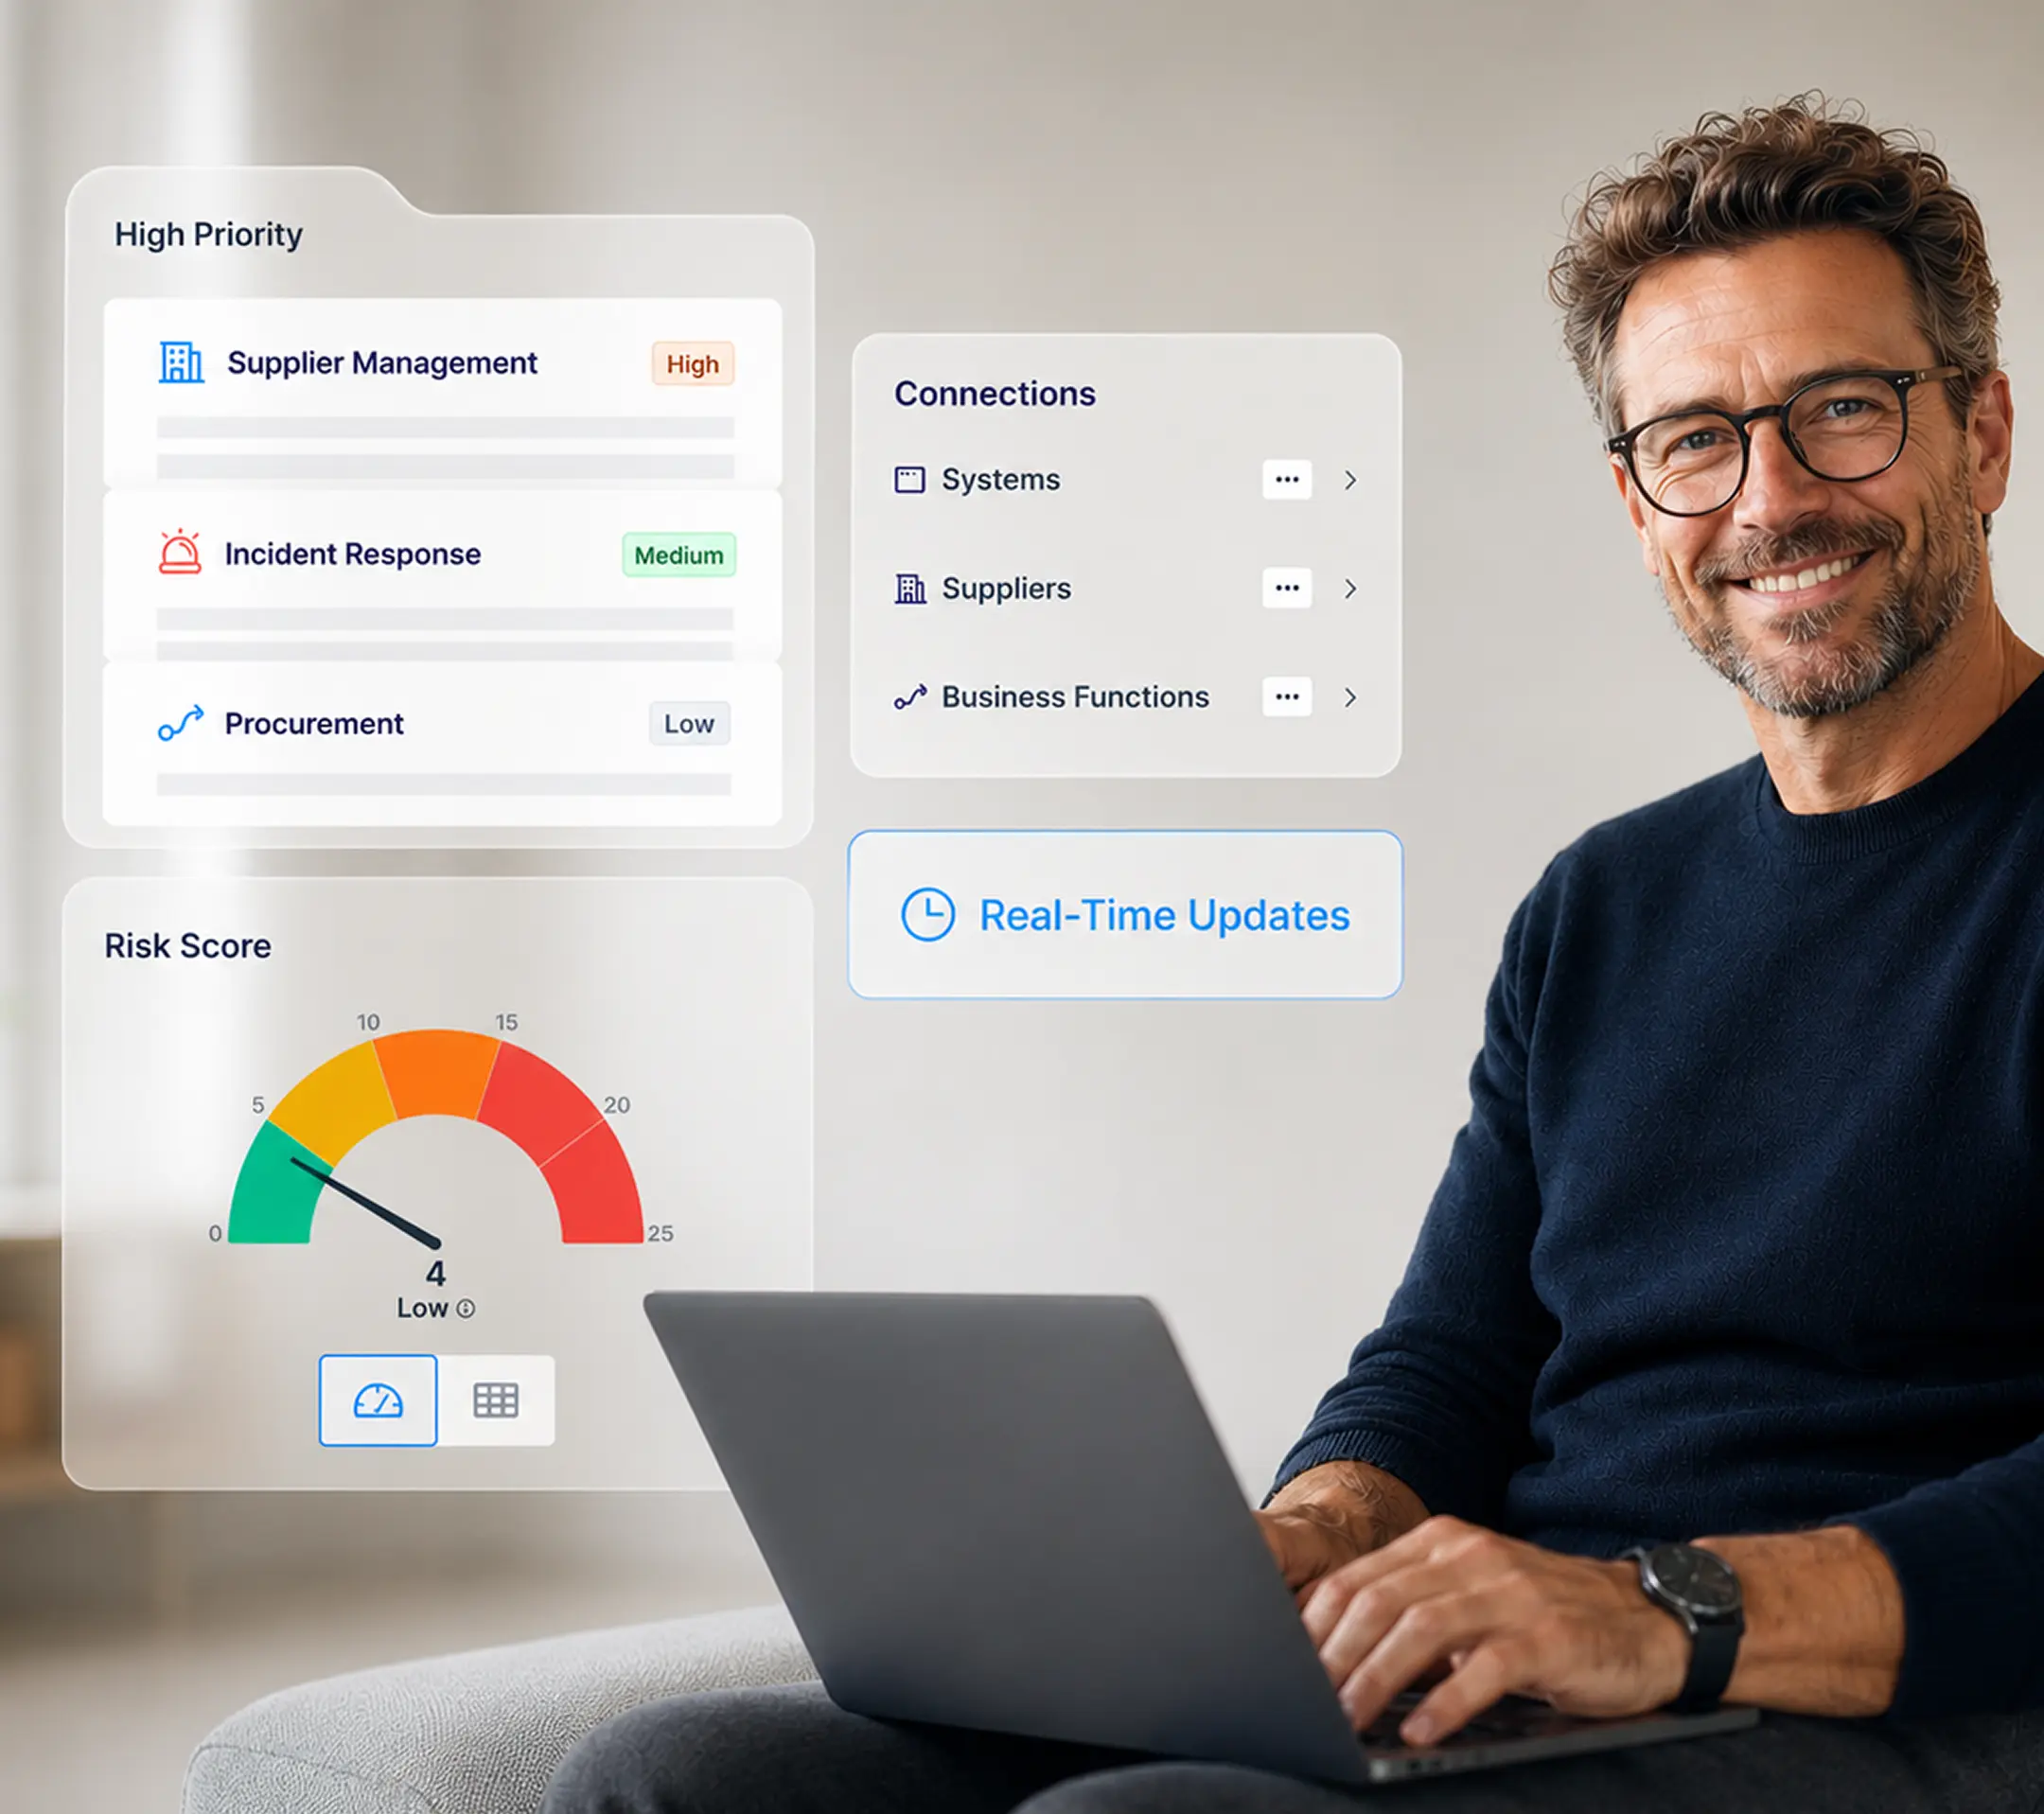
A GDPR compliance solution with real-time insight into your data and risk levels. Requirements are prioritized by risk and kept up to date with pre-populated regulatory content.




The cost of falling short on GDPR
Incomplete records
Art. 30 GDPR requires a documented record of every processing activity — one of the first things a regulator asks for during an inspection.
Up to €10M or 2% of turnover
Undocumented data subject requests
Data subjects have enforceable rights with statutory response deadlines. Art. 5(2) and Art. 24 require you to demonstrate compliance, not just claim it.
Up to €20M or 4% of turnover
Missing the 72-hour window
Art. 33 GDPR requires notifying the supervisory authority within 72 hours of becoming aware of a breach — one of the tightest deadlines in the regulation.
Up to €10M or 2% of turnover
Full GDPR coverage, without the scramble
See how compliance and legal teams use Formalize to move from scattered tracking to a single, audit-ready view of their GDPR obligations without adding headcount.
“With Formalize, we went live practically on day one. Within two months, we had full coverage of our compliance needs, even over the holiday season.”
Fernando Sanz de Galdeano
CISO, Arcano Partners
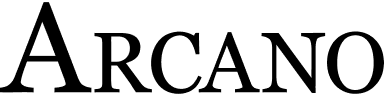
The manual way
-

Requirements, policies, controls, and risks sit disconnected from the assets, contracts, and people they actually apply to, traceability has to be reconstructed by hand, every time
-
Compliance status gets reported as a static snapshot someone has to assemble, a backward-looking, manually built picture, not a current one
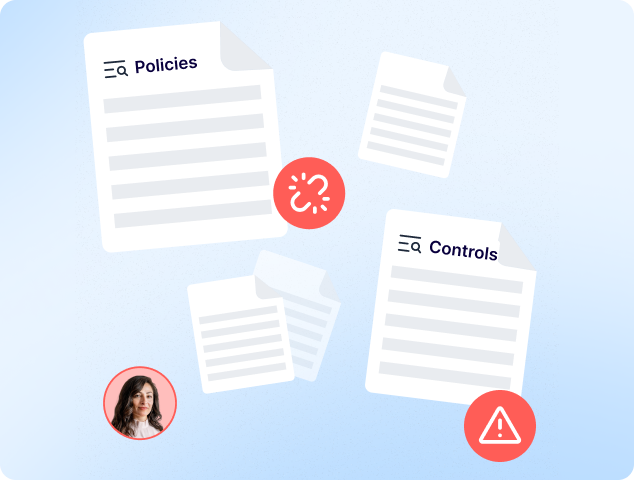
The Formalize way
-

Requirements, policies, controls, and risks are mapped directly to operational resources (assets, contracts, employees) in one unified environment where the links are already visible.
-
Statistics and reports generate in real time from actual platform usage a live view of the control system's strengths and weaknesses, ready for decision-making.
A GDPR tool that makes compliance part of how your organization runs
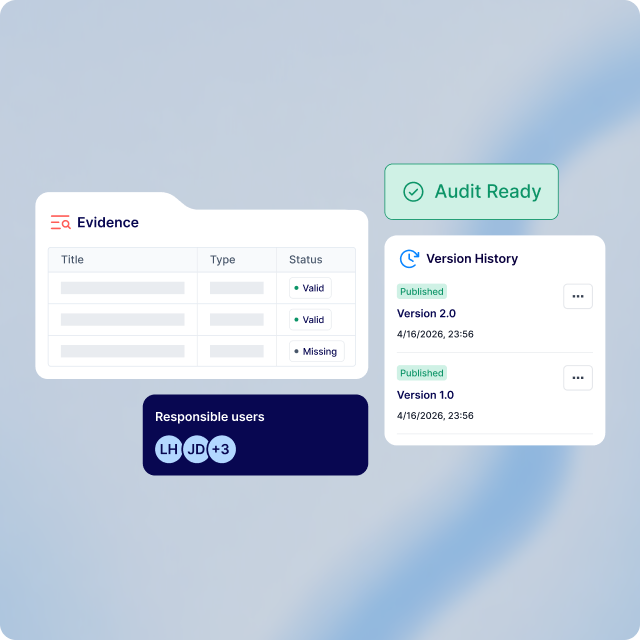
GDPR documentation
One audit-ready repository, not scattered files
Evidence, policies, and risk registers live in a single, standardized repository with strict version control and clear chain-of-custody — including your Art. 30 record of processing activities and your data subject request log (Art. 12, 15–22, 24, 5(2)), already structured to what a regulator expects to see.
-
Evidence, policies, and risk registers live in one place
-
Strict version control and chain-of-custody, so you can always show what changed and when
-
Art. 30 records and data subject request logs already structured the way a regulator expects to see them
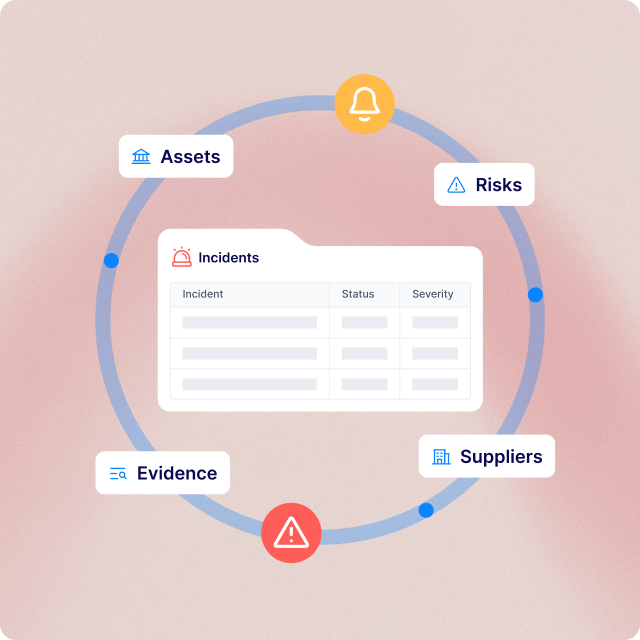
Incident response
Guided breach response, built for the 72-hour clock
When an incident happens, dynamic, context-driven questions walk your team through report creation instead of a blank form — built-in decision support classifies type and severity using ENISA's Methodology for the Assessment of Severity of Personal Data Breaches, so the 72-hour Art. 33 window becomes achievable, not a scramble.
-
Dynamic, context-driven questions replace a blank incident form under time pressure
-
Built-in severity classification using ENISA's methodology
-
Makes the Art. 33 72-hour window achievable instead of a scramble
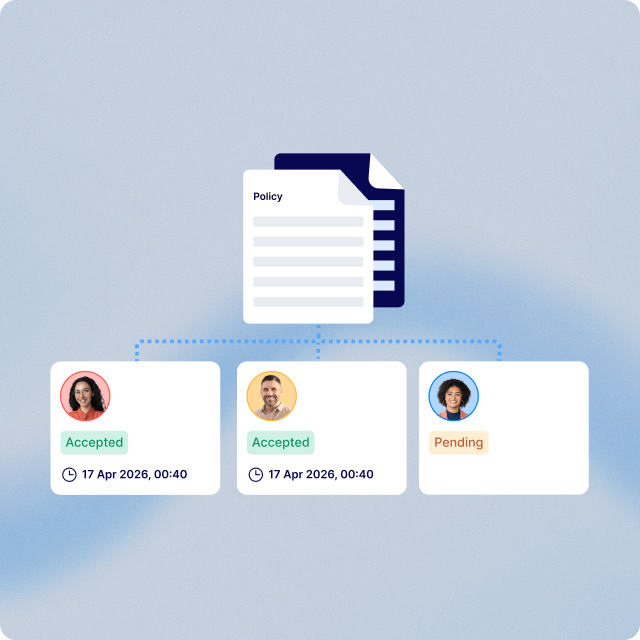
Workflow automation
Nudges that keep things moving, escalation when they don't
Native, targeted reminders keep compliance visible across departments without causing alert fatigue. When an action item stalls anyway, built-in escalation paths automatically loop in the right stakeholder, turning a missed deadline from a silent bottleneck into a shared, solvable problem.
-
Targeted reminders keep compliance visible across departments
-
Stalled action items automatically loop in the right stakeholder — no manual chasing
-
Missed deadlines become a shared, solvable problem instead of a silent bottleneck
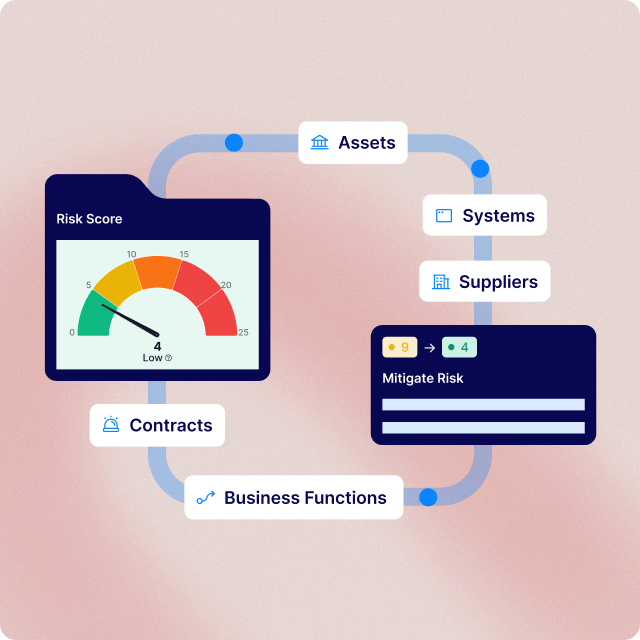
Risk assessment
Risk scoring that recalculates itself
Inherent Risk (Likelihood × Impact) and Residual Risk (Inherent Risk − Control Effectiveness) run on one standardized formula across every business unit — and update instantly whenever linked control or KRI data changes, eliminating broken spreadsheet formulas and inconsistent scoring between teams.
-
One standardized formula applied consistently across every business unit
-
Scores update instantly when linked control or KRI data changes — no stale numbers
-
Eliminates broken spreadsheet formulas and inconsistent scoring between teams
Part of a broader compliance foundation
GDPR is one of several frameworks that shape operational resilience. Formalize connects with other compliance and security requirements so organizations can maintain alignment across obligations.
1 / 4
Trusted with the data GDPR asks you to protect
A platform-wide logging system creates a transparent, verifiable record of every action across Formalize. All data is encrypted in transit and at rest, so it can't be altered, intercepted, or spoofed — accountability isn't something you have to take our word for.