
Maurice Müller
Senior Content Manager
Maurice Müller is a journalist and content strategist with experience across print and digital media. At Formalize, he translates complex compliance and regulatory topics into clear, practical content for compliance, risk, and security professionals across Europe.
Key takeaways:
"GRC software" covers three different kinds of product: enterprise risk platforms, audit-led systems and compliance automation tools. Decide which one you need before you compare vendors.
Your main workload should drive the choice: enterprise risk, internal audit, several frameworks at once, security certification or supplier oversight.
All six vendors in this comparison price on request, so licensing questions belong in the first demo, not the last.
Ask every vendor to show your own workflow before any custom configuration, and to explain how you'd export your data and audit history if you leave.
Search for "best GRC software" and you'll find lists that put very different products side by side. Some are built to run risk for a global bank across hundreds of business units. Some are built around the internal audit plan. Others exist mainly to get a SaaS company through its first SOC 2 report. All of them are sold as governance, risk and compliance (GRC), and comparing them on one long feature list tells you very little. Practitioners asking for advice tend to raise the same concerns: how long implementation really takes, whether licensing stays predictable as the program grows, and whether they need a dedicated GRC platform at all. This comparison is built around those questions.
How we evaluated the GRC platforms
We picked six platforms that between them cover the main types of GRC software: enterprise risk platforms (ServiceNow IRM and Archer), an audit-led system (Optro) and compliance tools, from multi-framework programs (Hyperproof) to security automation (Vanta). Formalize connects risk, compliance and supplier oversight across European frameworks.
We compared the platforms on eight dimensions, based on what each vendor documents on its own website:
Risk management: assessment methods, ownership, treatment and reporting.
Controls and compliance: requirements, policies, control testing, evidence and framework mapping.
Internal audit: planning, requests, findings and remediation.
Third-party risk: supplier assessments, linked risks and ongoing reviews. Our guide to supplier risk management covers what good looks like.
Workflows and accountability: approvals, notifications, history and role-based access.
Reporting: views that work for practitioners, executives and the board.
Implementation: configuration, integrations, migration and support.
Commercial fit: how licensing is structured, and which modules or services cost extra.
For an independent reference, Gartner Peer Insights lists features such as risk assessment methodologies, interoperability, data visualization and reporting, and frameworks and controls mapping for this market. We used it as a cross-check, not as a scoring model.
A note on method: this is a comparison of documented product fit, not a hands-on test of every platform. Formalize is our own product, so we've stuck to what each vendor publishes about itself, with a source and a date for every platform. Features change quickly, so confirm anything that matters in a demo, and see for yourself how our connected GRC system works.
Six GRC platforms compared
Quick picks by use case. These are editorial fits based on what each vendor publishes, not test results:
Risk, compliance and suppliers connected across European frameworks: Formalize
IT and security workflows already on ServiceNow: ServiceNow IRM
Complex enterprise risk programs: Archer
Programs led by internal audit: Optro
Compliance operations across many frameworks: Hyperproof
A first SOC 2 report or ISO 27001 certificate: Vanta
Platform | Best for | Primary strength | Risk, compliance and audit focus | Third-party oversight | Implementation support | Check in the demo |
|---|---|---|---|---|---|---|
Mid-market and regulated organizations working across European frameworks | Risks, controls, evidence, suppliers and approvals in one connected system | Mainly risk and multi-framework compliance; audit module for internal audits | Supplier assessments, contracts and evidence linked to risks | Guided setup with Compliance Blueprints, assisted migration of existing data | Integrations for evidence collection, if SOC 2 is the goal | |
Organizations already running on ServiceNow | Risk and compliance on the same platform as IT and security workflows | Mainly IT and operational risk; audit management available | Separate third-party risk management application | ServiceNow experts and implementation partners | Licensing and setup effort if you don't run ServiceNow yet | |
Large enterprises with complex risk programs | Enterprise risk across operational, IT and third-party risk | Mainly enterprise and regulatory risk; audit management available | Third-party governance product | Archer and implementation partners | Configuration effort and who maintains it after go-live | |
Optro (formerly AuditBoard) | Programs led by internal audit | Audit planning and workpapers connected to risk and compliance | Mainly internal audit and SOX-style controls | TPRM module | Optro Success and Services | Depth of risk and supplier workflows outside internal audit |
Multi-framework compliance and assurance programs | Shared controls across a large framework library | Mainly compliance and assurance; risk registers linked to controls | Vendor risk management module | Dedicated support team | Depth of enterprise risk and internal audit workflows | |
Startups and SaaS companies preparing for SOC 2 or ISO 27001 | Automated evidence collection through integrations | Mainly security compliance | Vendor discovery and risk assessment | Onboarding support; Vanta cites weeks rather than months | Risk, audit and governance depth beyond security compliance |
All six platforms are quote-based, and Formalize also offers a free plan and a 14-day trial. Vendor details checked on 22 October 2026 on each vendor's own website.
The leading GRC software platforms
Each profile below covers who the platform is best for and its key capabilities, based on the vendor's own website. Formalize gets a longer walkthrough further down, with screenshots, because it's the one product we can show from the inside.
Formalize: for connected risk, compliance and governance workflows
Best for: mid-market and regulated organizations, including financial entities, that manage several European frameworks such as NIS2, DORA, ISO 27001 and the GDPR, and need to show leadership how decisions were made.
Key capabilities: Formalize links every risk to the systems, suppliers, contracts, assets and business functions it affects, and scores it on your own matrix for inherent and residual risk. Governance tasks run as workflows with named owners and timestamped approvals. Supplier assessments, contracts and evidence sit next to the risks they introduce. Compliance Blueprints cover NIS2, DORA, ISO 27001, ISO 22301, the GDPR and more, and the Audit module runs internal audits structured to the IIA Global Internal Audit Standards. Formalize is hosted in the EU (AWS Frankfurt).
Source: formalize.com/en/grc
ServiceNow IRM: for organizations already running on ServiceNow
Best for: organizations that already run IT service management, security operations or other workflows on ServiceNow and want risk and compliance on the same platform.
Key capabilities: ServiceNow describes Integrated Risk Management (IRM) as connecting "risk and compliance across IT, cyber, and business operations in one system of action." It runs on the ServiceNow AI Platform. Audit management and policy and compliance management are offered within its GRC family, and a third-party risk management application covers the supplier lifecycle "from onboarding to retirement." For EU buyers, ServiceNow promotes DORA-aligned third-party risk management and reporting.
Source: servicenow.com: Integrated Risk Management
Archer: for complex enterprise risk programs
Best for: large enterprises, particularly in financial services, energy, healthcare and the public sector, where a central risk function runs several risk disciplines at once.
Key capabilities: Archer names the chief risk officer, chief compliance officer, head of internal audit and CISO as the roles it serves, and says more than 1,500 organizations run on it. Its Archer Evolv portfolio covers operational, IT, third-party and enterprise risk, with products for audit management, third-party governance, operational resilience and regulatory change. For regulatory change, Archer says it monitors more than 22 million regulatory sources and maps changes to controls.
Source: archerirm.com: Products
Optro: for audit-led GRC programs
Best for: organizations where internal audit drives the platform decision, including teams with SOX or extensive internal controls testing.
Key capabilities: Optro is the new name of AuditBoard, which rebranded in March 2026. Its audit capabilities include building "a risk-based plan across your audit universe," AI-drafted workpapers with cited evidence, and board-ready reporting. CrossComply covers compliance with a library of more than 30 frameworks, including SOC 2, ISO 27001 and the GDPR, and a TPRM module turns high-risk vendor findings into remediation tasks. Optro says every AI-supported step needs a person to approve it.
Source: optro.ai: Platform
Hyperproof: for multi-framework compliance and assurance programs
Best for: compliance and assurance teams, from mid-market to enterprise, running several frameworks in parallel.
Key capabilities: Hyperproof says it supports more than 160 frameworks, including SOC 2, ISO 27001, DORA, NIS2 and the GDPR, and lets teams "standardize control operations across multiple frameworks to minimize redundancy." Control health data feeds into risk registers, and vendor risk management is part of the platform. Its AI features recommend control mappings and draft evidence requests, with human review.
Source: hyperproof.io: Product
Vanta: for security compliance automation
Best for: startups and growing SaaS companies whose first goal is a SOC 2 report or an ISO 27001 certification.
Key capabilities: Vanta's core is automated evidence collection. It says it "automates up to 90% of the evidence needed to prove compliance" through more than 400 integrations, with automated tests that monitor controls hourly. It lists more than 35 frameworks, including SOC 2, ISO 27001, the GDPR, NIS2 and DORA, and also covers vendor discovery and vendor risk assessment.
Source: vanta.com: Trust Management Platform
Vendor details checked on 22 October 2026 on each vendor's own website. For the questions worth asking every vendor, see the demo checklist below.
Which GRC platform fits your organization?
Startups and growing SaaS companies
If a customer is asking for a SOC 2 report this quarter, evidence automation is the priority, and a tool built for that is usually the fastest route. Not every startup needs an enterprise GRC suite. The picture changes as you grow. Once you hold ISO 27001, sell to regulated customers or face NIS2 obligations, you need risks, policies and management decisions that connect to your controls, not just passing tests. Plan for that step when you choose, so you don't have to migrate a year later. Formalize supports SOC 2 and ISO 27001 alongside its European frameworks.
Mid-market teams managing several frameworks
When you run SOC 2 and ISO 27001, or ISO 27001, NIS2 and the GDPR at the same time, the main risk is doing the same work twice. Look for controls, evidence and owners managed once, in one system, with each framework showing its own view of them. Take incident handling: the procedure, owner and incident log you keep for ISO 27001 are also the starting point for NIS2, and you add what NIS2 asks for on top, such as significance criteria and the 24-hour early warning. Our ISO 27001 to NIS2 gap analysis shows where else that applies. Check framework depth, not just the logo list: a framework library can mean a full set of requirements with guidance, or a list of headings. Supplier oversight belongs in the same place, because most frameworks now ask how you manage third-party risk.
Large enterprises with complex risk and audit programs
Enterprises need a platform that mirrors their structure: legal entities, business units and regions, each with its own owners, and reporting that rolls up to group level. Ask how the platform handles your risk methodology, including scoring models and appetite, and how internal audit uses the same risk data rather than its own copy. Configuration is where these projects succeed or stall. Ask who will maintain the platform after go-live, and how much of that work your own team can do. See how Formalize approaches enterprise risk with Risk Intelligence.
Teams whose primary need is vendor risk or internal audit
Sometimes one workflow matters more than everything else. If supplier assessments dominate your workload, for example ICT third-party risk under DORA, weigh the vendor risk workflow most heavily: onboarding, questionnaires, contract data, monitoring and remediation. If the audit plan drives your year, an audit-led platform may suit you better than a broad GRC suite. Either way, check that the specialist workflow connects to your wider risk and control data, or you'll end up with a second spreadsheet.
What should you check in a GRC software demo?
Ask every vendor to show these with your own example, not a prepared script:
How much of our workflow works before any custom configuration?
Can our existing controls, evidence and history be migrated, and who does that work?
How do permissions protect sensitive risk, incident and audit material?
Which integrations are included, and which cost extra?
How are additional users, frameworks, entities, suppliers or modules priced?
Can we export all our data, including audit history, if we leave?
Where does AI assist, and which decisions still need a person to approve them?
To compare like with like, give every vendor the same scenario. For example: a new critical supplier gets a high risk score. Ask each vendor to take it from the supplier assessment to an approved treatment decision, and to end with the view your management would see, including who approved what and when.
See Formalize with your own use case
Bring a risk, a framework or a supplier you're working on. We'll show you how it runs in Formalize, from the first assessment to the report for your management.

See how Formalize connects risk, controls and evidence
It starts with a risk assessment: the risk is scored on your own matrix, with inherent and residual values, and linked to the suppliers, systems and business functions it affects. It gets a named owner.
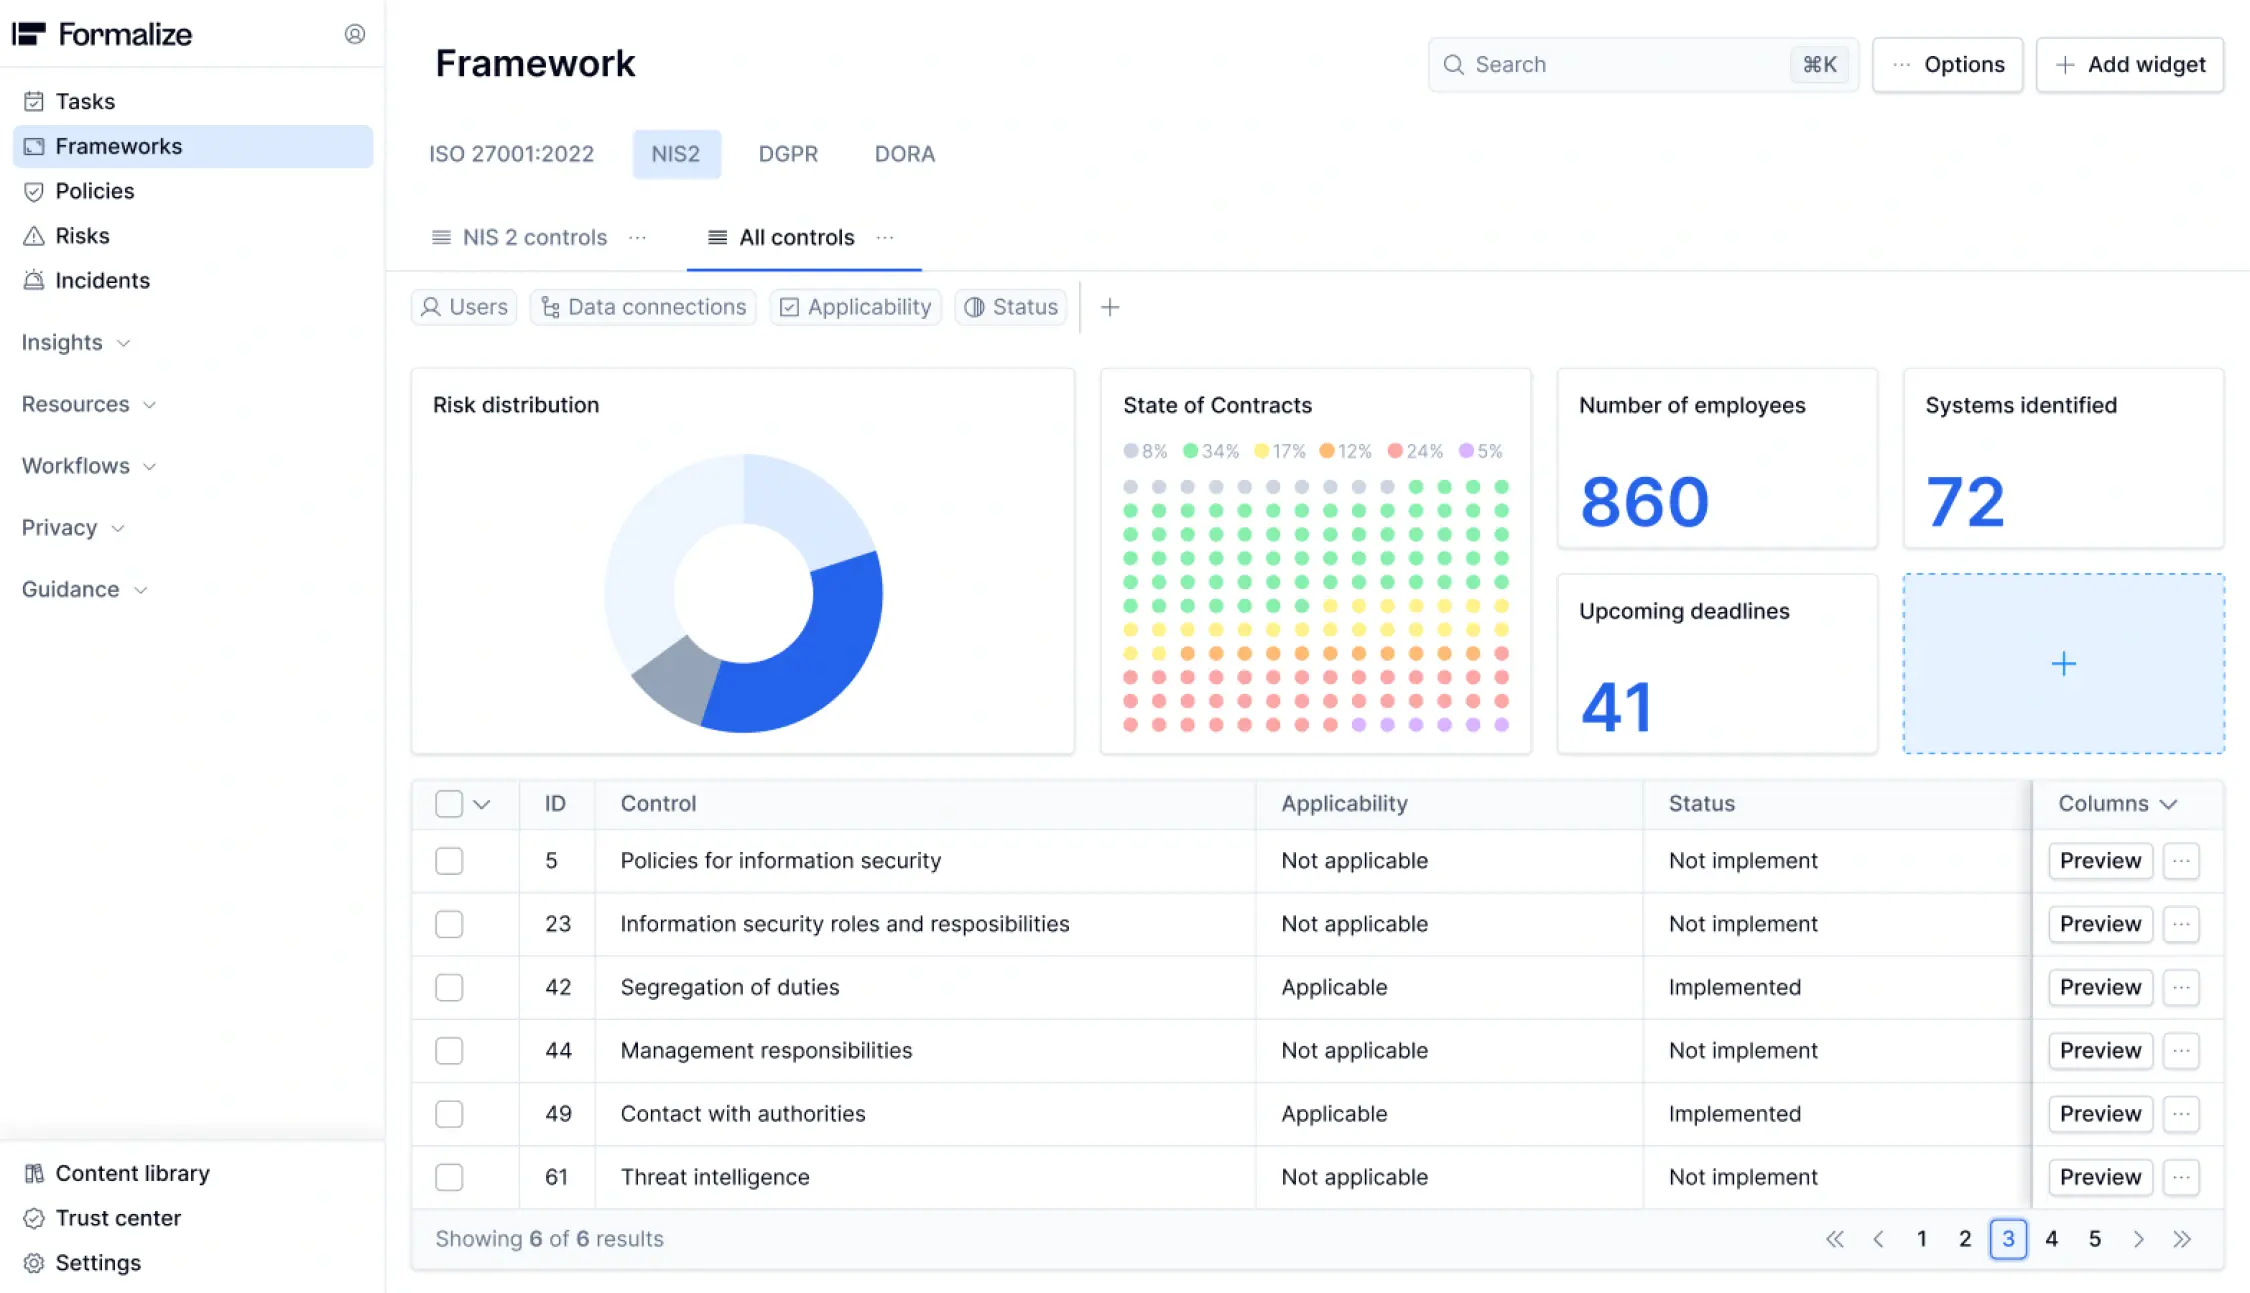 The owner links it to a control, mapped through framework and control management to the requirements it supports. Evidence is uploaded against the control, and the decision to accept or treat the risk goes through an approval workflow, timestamped and attributed. The status then shows up on the dashboard leadership reviews, with the approval trail behind it.
With Formalize, we went live practically on day one. Within two months, we had full coverage of our compliance needs, even over the holiday season.
Fernando Sanz de Galdeano, CISO, Arcano Partners
If you want to see that sequence with your own risks and frameworks, explore the Formalize GRC platform or book a walkthrough.